

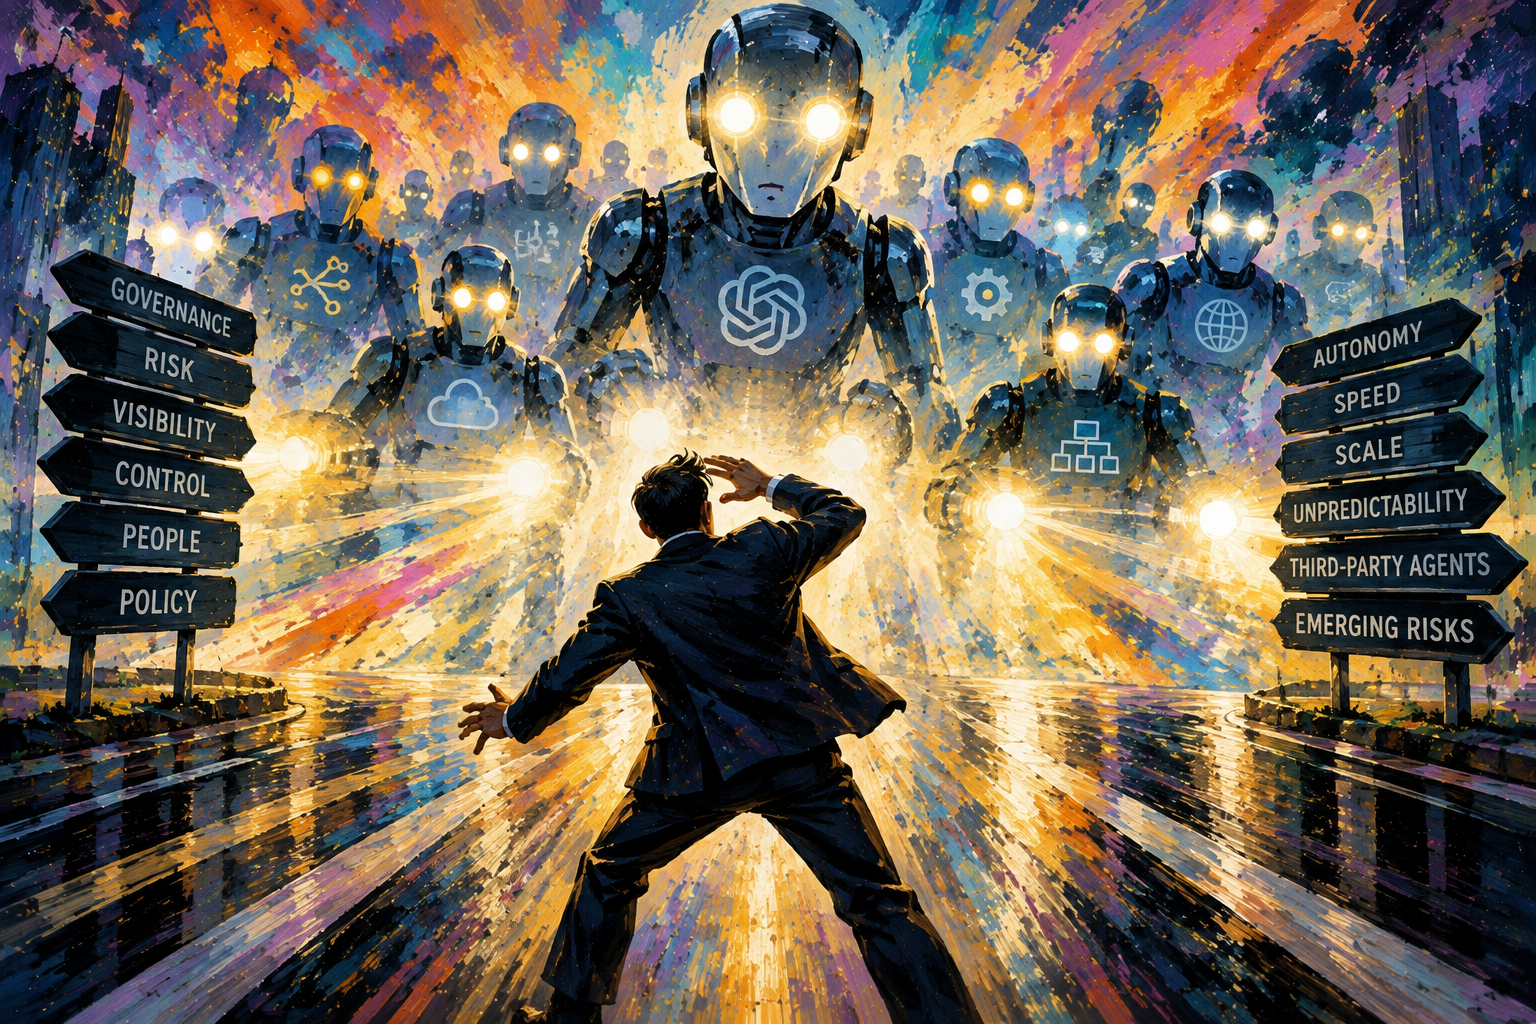
Caught in the headlights: how can CISOs manage a problem like agentic AI?
In Partnership With
CISOs have been managing a continually shifting technology landscape all their careers. It comes with the territory. But few could argue that the speed of AI’s rise has been dizzying for many in the industry. PwC reckons 61% of CEOs are actively investing in the technology today, although the real figure is likely to be higher. Now the next stage in AI’s inexorable advance is here, and it’s making security leaders nervous.
Several of them gathered together for a RANT roundtable recently to discuss all things agentic AI.
“I don’t think there’s a bigger, more impactful mainstream problem,” said Bob Horn, CRO of our hosts for the evening, Reco. “We’ve seen a lot of technology shifts, but I don’t think we’ve seen one move this fast with this much uncertainty for the world.”
Horn opened proceedings by describing the three different ways that CISOs are responding to this disruption. First is the security leader who says, “I’m too old for this” and refuses to change. Second is the CISO who mistakenly believes that their current playbook will still be effective in managing agentic AI risk. And third is the one who understands that people, process and technology must change.
Can someone please turn the lights on?
Fortunately, no cybersecurity leaders around the table seemed to fall into the first category. Their mere attendance was proof of that. But there was a certain amount of despair on show at the speed, scale and complexity of the challenge.
Our speaker for the evening, IP Finance International CISO, Nick Jones, bemoaned the fact that cyber leaders increasingly seem out of the loop.
“We have unsupervised interns; AI agents in charge of AI agents. It’s shadow IT on steroids,” he argued. “I need an inventory and I need visibility. I need the lights turned on.”
Others agreed that visibility is a key challenge as agents begin proliferating in the enterprise. “We have internal AI, external AI and no doubt there’s shadow AI too,” said one.
Several others expressed alarm that the business is moving too quickly, but also that blocking their projects outright is not an option.
“The problem is we’re back to the old days of the ‘department of no’,” said one. “We’ve become the speed bump again and that’s a difficult PR thing to manage.”
Overprivileged and over here
Various views were shared as to why agentic AI poses such a threat to organisations. They boil down to: visibility, identity and connectivity. Reco’s Horn suggested that there may be tens of thousands of agents running in an enterprise, but only a small number have access to sensitive environments. That makes tracking and managing everything critically important. “Every agent could be a crown jewel,” he argued.
Others aired concerns about over-privileged agents, unmanaged plugins, and the potential for autonomous machines to cause irreversible damage.
“The attack vectors haven’t fundamentally changed. It’s the speed and broadening of the attack surface that have,” said one CISO. “They can be profoundly dangerous if we don’t manage what they’re capable of doing.” Another agreed that the velocity of change is causing sleepless nights. “We’re not prepared for the aftermath,” they warned.
One CISO raised a red flag over MCP. Having just got a handle on securely managing the organisation’s APIs, he fretted that the protocol could open up a new attack surface and route to data exfiltration.
Where resilience meets regulation
Several attendees shared their anxieties over regulatory scrutiny, and how the complexity of agentic environments makes it difficult to answer auditor’s questions.
“They’ll ask you a simple question like ‘can you see what’s doing what?’ But you’ll need to connect to 25 different systems to give them an answer,” said one CISO.
IP Finance International’s Jones explained that regulators are looking for better governance and monitoring; the latter because “guardrails you use today may need to look different tomorrow”. However, if those controls are too rigorous, “people will just work around them”, argued another attendee.
Others were sceptical about whether regulators are even sufficiently clued up to know what questions to ask.
“Regulators want to address AI and quantum but they’re struggling with how they keep pace,” said one CISO. “The speed of regulation is actually slowing.”
However, that doesn’t mean companies will be let off the hook. Jones confided that a recent regulatory letter had been “quite punchy”. He added: “they might not know what they’re looking for but they’re coming.”
As agentic projects expand, resilience is likely to be top of the agenda for auditors, Jones continued. Others around the table sounded the alarm around similar themes – such as what happens if critical business services come to rely on agents, but then underlying models change or are replaced by vendors.
Back to basics, to the future
Despite the general wringing of hands, some CISOs were bold enough to suggest some approaches to securely managing the growing agentic fleet in many enterprises. One advocated a “back-to-basics” approach, acknowledging that agentic AI amplifies existing risks rather than creates new ones.
“In the cloud identity is everything-it’s your perimeter-and I think with AI it’s the same,” he said. “Fundamentally we need to go back to basics. Get your hygiene; sort your IAM.”
However, Reco’s Horn pointed out that there are “toxic combinations” that may complicate this approach, citing the challenge of managing connected AI systems such as Copilot and Agentforce. In this way, one AI could expose data associated with another to attackers if not properly configured.
Others suggested a human in the loop was a useful approach, although some attendees warned that we’re fast approaching a time when the sheer volume of data and decisions presented to humans may make such a model unworkable.
Which brings us back to Reco’s Horn, who ended proceedings with a checklist for CISOs to work through. As a starting point, they need to understand what they have, who’s using it, what it’s connected to and what it’s doing, he said. Then comes the hard part: figuring out what to do about it.
As tough as today’s agentic environment is to manage, CISOs must also think about what’s coming down the track. “This is not a destination, this is a journey,” Horn concluded. “You’ve got to catch up. And whatever vendor you choose; buy for the future as well as the present.”
See every agent. Know what it can reach. Fix the risk before it becomes an incident.
Reco discovers every agent and identity across your environment, scores real risk instead of raw alert volume, and remediates by routing findings, scoping access, and revoking what shouldn’t exist. One platform, complete agent security. Demo Reco today [https://www.reco.ai/demo-request]